Know the real gaps
Map controls to systems, processes, owners, evidence, and business risk.
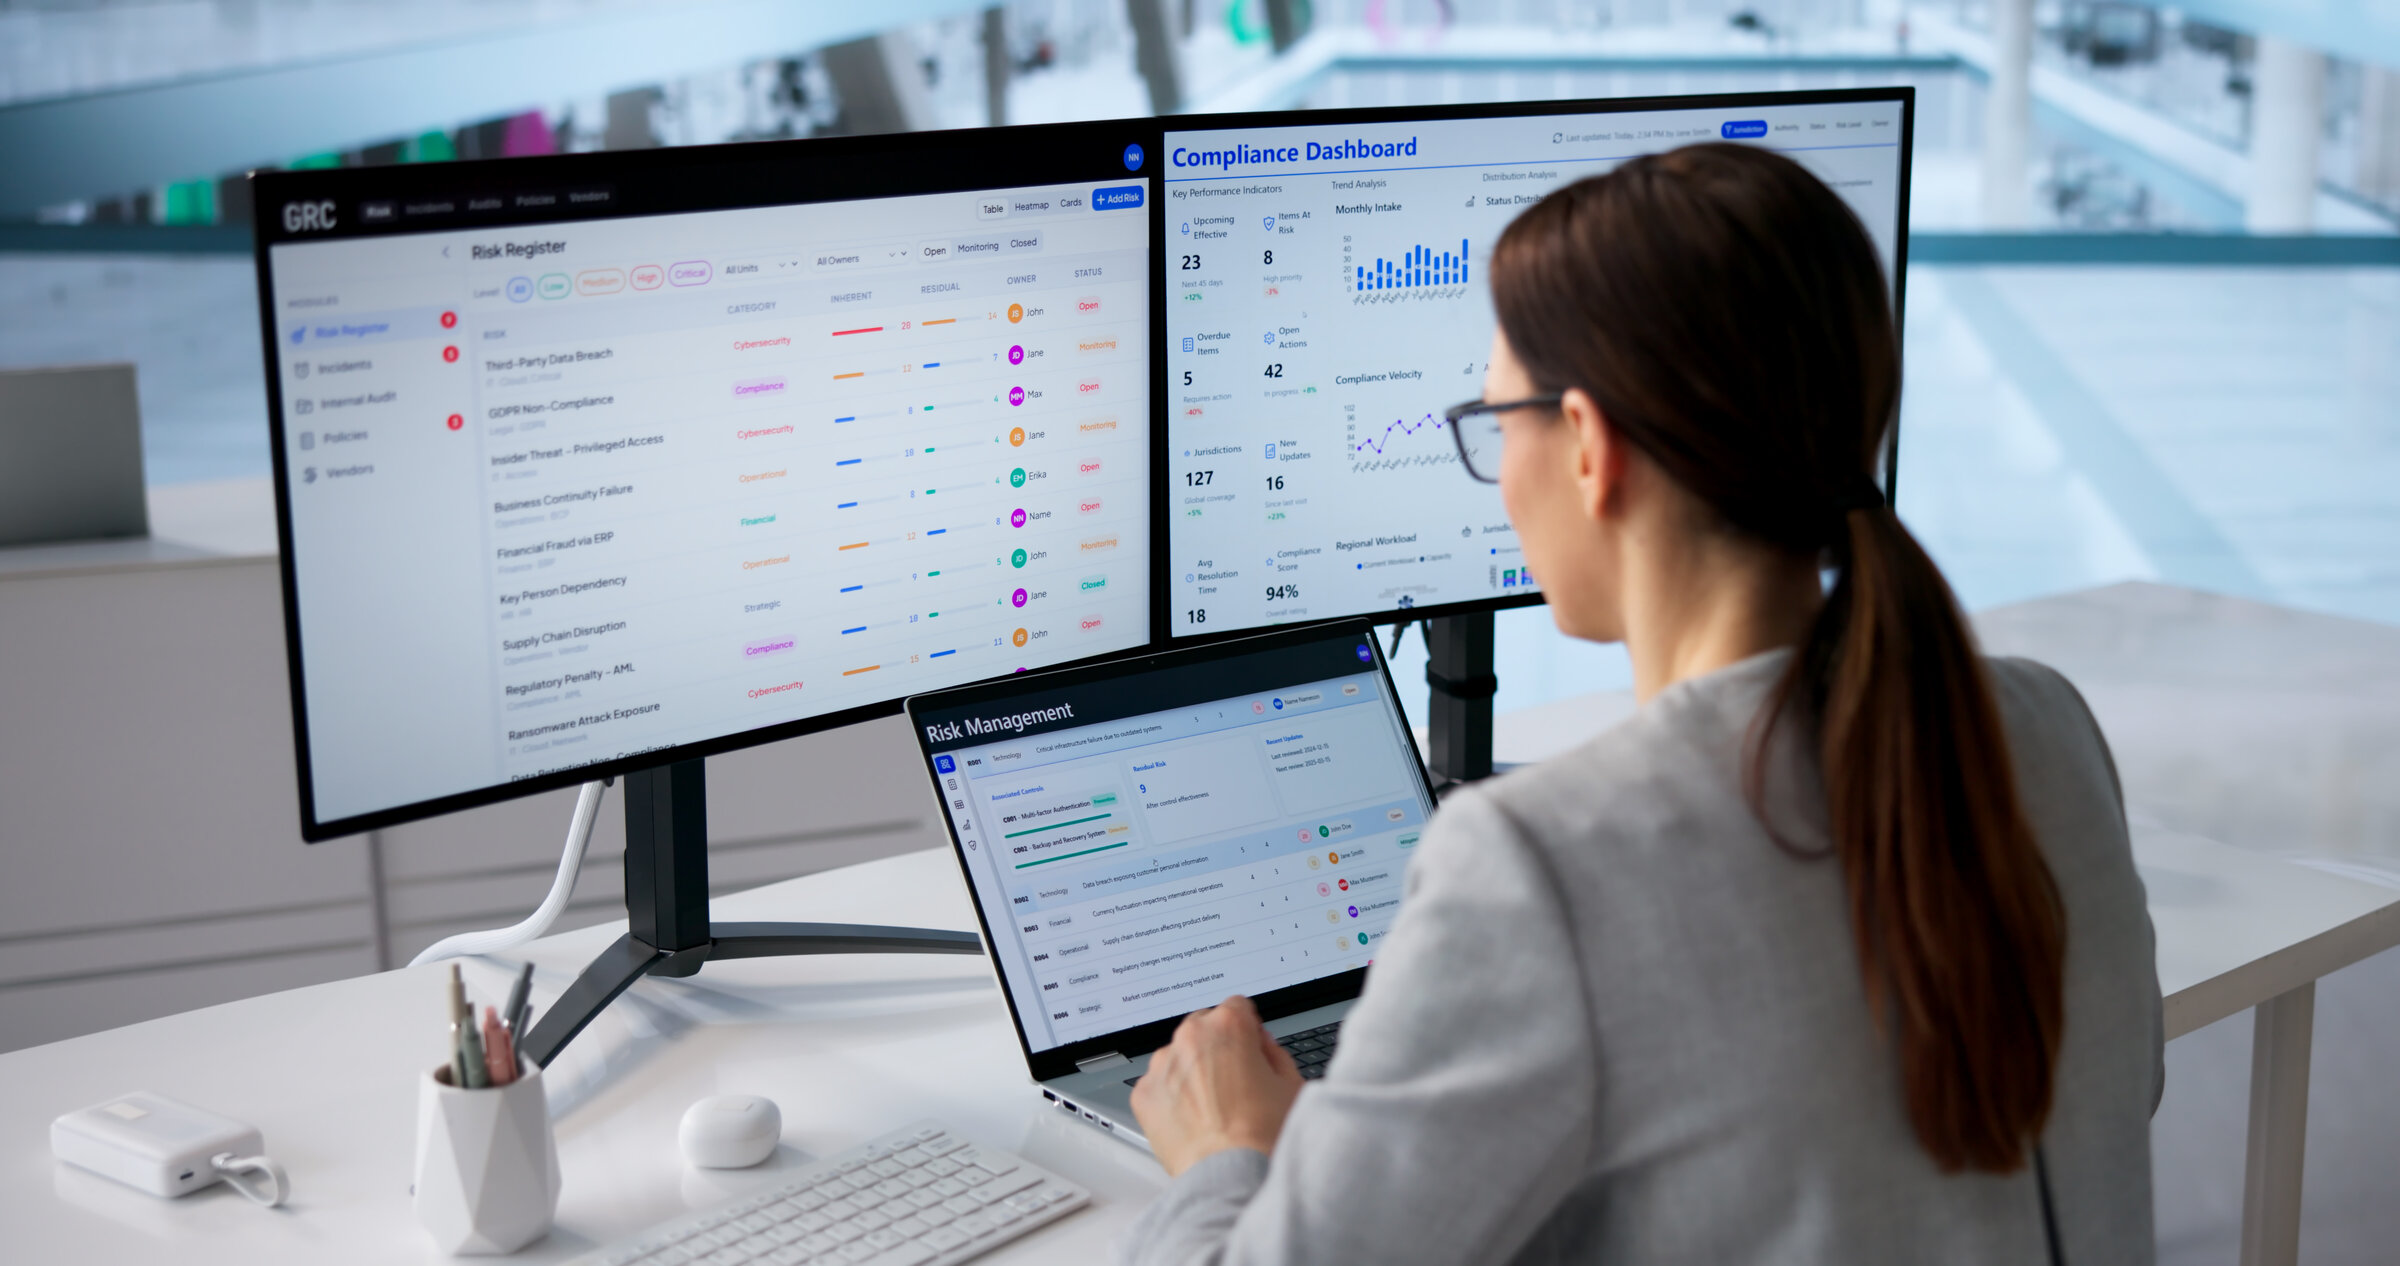
Move from recurring audit scramble to continuous readiness.
Expert guidance for SOC 2, ISO 27001, ISO 42001, CMMC, and more, from first assessment through every audit cycle.
Map controls to systems, processes, owners, evidence, and business risk.
Prioritize changes that improve both audit readiness and security posture.
Get hands-on support throughout audit preparation, auditor coordination, and the audit itself.
Use managed compliance to monitor controls, optimize your GRC platform, and prepare continuously.
We don't just advise on compliance. BlueAlly maintains SOC 1 Type 2, SOC 2 Type 2, ISO/IEC 27001, ISO/IEC 42001, ISO 9001, CMMC Level 2 (C3PAO assessed, 110/110), and CMMI Level 3 ourselves.
Visit our Trust CenterScope requirements, evaluate controls, and create an actionable roadmap.
Professional ServicesImplement technical, policy, process, and evidence improvements.
Cybersecurity expertiseOrganize control ownership, evidence, testing, and auditor coordination.
Extend your teamContinuous monitoring, evidence workflows, policy upkeep, and advisory support.
Managed ServicesNeed a senior leader to own the program between audits? vCISO & vCIO Advisory
Readiness, remediation, audit support, and managed compliance for the frameworks your customers and regulators expect.
We implement and optimize the GRC platforms you run, and coordinate with independent auditors through every cycle.
One sustainable compliance model after acquisition.
Read the story
PCI compliance restored through coordinated controls.
Read the story
A clean external audit after BlueAlly implemented 93 Annex A controls and built the company's ISMS.
Read the story
The tool saves roughly 10-17 engineering hours each month, standardized evidence, reduced manual error, and reached ROI in under a year.
Read the story
Technology firm improves sales performance by implementing centralized systems for compliance management.
Read the story
Financial institution implements comprehensive risk assessments and management tools to ensure industry compliance.
Read the story
The bank gained a trusted customer view for pricing and cross-sell decisions, delivered inside its rigorous security and compliance lifecycle.
Read the story
Cloud security provider achieves SOC 2 compliance through expert guidance and consulting services.
Read the story
Public school system improves security and compliance for Microsoft 365 using managed protective services.
Read the story
A comprehensive risk assessment identified gaps and remediation priorities for CMMC readiness.
Read the story
Healthcare organization reduces software licensing costs through professional infrastructure and collaboration assessment.
Read the story
Nonprofit organization modernizes Microsoft 365 security to meet compliance and data protection standards.
Read the story
Technology company secures digital assets by performing risk assessments and managing information security systems.
Read the story
System capacity doubled within hours, eliminating voicemail bottlenecks without disrupting live operations.
Read the story
Energy organization migrates security architecture to achieve and maintain necessary regulatory compliance.
Read the story
Organization transforms risk management and regulatory compliance processes using OneTrust software platforms.
Read the storyStart with an assessment, remediation plan, or managed compliance conversation.